Not necessarily.
This is quite straightforward:
Two things:
often get mixed up.
Anthropic says:
Claude Connector:
inherits:
your original system:
permissions.
For example:
If in Google Drive:
you can’t see:
a specific document,
then using Claude:
won’t suddenly grant you access.
If in any business system:
you don’t have permission:
to modify a record,
Claude:
won’t arbitrarily escalate your rights.
This is good.
But:
"AI won’t bypass existing permissions"
does NOT mean:
"the existing permissions are perfectly set."
The problem often isn’t Claude having too much access
but rather:
people originally having too much access.
Imagine a 5-person small company.
The boss,
for convenience,
shared the entire company Google Drive folders
with the administrative colleague.
Accounting data,
customer info,
contracts,
marketing materials,
HR files—
all accessible.
Previously,
this person might have only
opened a few of these folders daily,
so excessive permissions didn’t cause an immediate problem.
But AI Connectors change what "visible" really means
Just because someone:
has permission,
does not mean they actually:
search through all 5,000 files daily.
AI, however,
excels at:
cross-referencing,
searching,
organizing,
and comparing data across multiple sources.
What was originally:
"theoretically accessible"
can, with AI connected, become:
"one command to find information across many places."
This is a new distinction.
For example, if you only need to create a Monday Brief
The actual necessary data may include:
last week's sales,
cash flow,
overdue invoices,
pipeline status,
and calendar entries.
But if the connected account can also see:
payroll data,
employee records,
private customer contracts,
or unrelated project files,
then Claude isn’t overstepping,
but the workflow:
may still have access to a broader dataset than necessary.
Therefore, "no over-permission" and "least privilege" are not the same
The first question is:
Has the AI surpassed system limits?
The second question is:
Does the workflow actually need access to so much data?
These are two entirely different considerations.
Anthropic's rules on Connectors are very clear
Claude:
inherits:
each person's original permissions from the source system.
If:
the user can’t see a file,
a channel,
or a record,
the connector:
won’t grant it.
This means:
Claude won’t:
automatically become an admin
just because it’s connected.
But the official guidance also reminds of another point
When you connect a service,
you’re essentially:
authorizing Claude:
to access, and even modify,
data according to the connected account’s permissions.
So the account’s permissions:
form the first line of defense.
If this boundary:
is too broad,
the connector simply follows it.
For example, a shared Google Account
This is common in small companies
for convenience.
Everyone :
uses the same account.
Drive, calendar,
and email are all shared.
It seems convenient,
but once:
this account is connected to AI,
AI inherits:
all the data accessible to that shared account.
So you shouldn’t just ask, "Is Claude safe?"
You also have to ask:
"Whose account am I connecting with right now?"
What files, emails, calendars, records, and payment data
can this account access?
These really determine:
the AI’s data boundaries.
The second thing to check: what actions are enabled for the connector
Permissions on data are one layer,
action permissions are another.
For example, a Google Drive connector
may have:
read access,
as well as:
move, share, trash, or create permissions.
All on Drive,
but the risk is vastly different.
Anthropic now lets team/enterprise admins impose restrictions
They can set connector tools to:
Always allow,
Needs approval,
or Blocked.
Connectors can be limited to read-only, for example:
Claude can search and summarize emails,
but cannot send emails.
Claude can read Drive files,
but cannot create, edit, or move them.
This layer is very important
Because:
Source system permissions answer:
"Can this person do it?"
But connector restrictions answer:
"Even if the person can, should AI be allowed to?"
For example:
The boss has full QuickBooks permissions,
but Monday Brief only requires read access.
So AI doesn’t need write access.
This is a more mature AI permission design
Not simply copying a person's full ability,
but carving out only what the workflow truly needs.
If a person can do 10 things,
AI only needs 2,
then only grant those 2.
The third point: approval is about actions, not data access
This can be confusing.
Approvals usually control:
actions—
such as send, delete, move, or write.
Before executing,
approval asks for confirmation.
But:
the scope of readable data
often requires a different permission layer.
If AI is allowed to read a file,
you can’t assume setting all write actions to “needs approval”
also restricts read access.
It doesn’t.
Therefore, read-only does not mean zero risk
Read-only is indeed safer
than write access,
because AI can’t modify, delete, or send.
But if AI can read unnecessary sensitive data,
it still means the workflow has too much access.
For example, a marketing report
does not need employee salaries.
So don’t let that workflow use an account
that can see all HR data.
The fourth point: AI can combine data across sources
This is something traditional permission design
needs to reconsider with AI.
A single piece of data
may seem harmless alone.
For example, calendar data
contains client names,
CRM has transaction status,
emails contain negotiation details,
accounting shows actual amounts.
AI excels at
assembling these multiple sources together.
None of the systems individually are "overstepping"
but combined,
the information density
may become very high.
This is called
Data Aggregation Risk.
Simply put:
What humans needed four systems to piece together, AI now does in one query.
Therefore, the more connectors,
the more critical it is to ask
if they all really need to be connected.
The fifth point: shared folders may have long-accumulated permission drift
Many companies’ Google Drive,
Notion,
Slack,
after 3 or 5 years,
with staff coming and going,
shared folders have been shared and reshared,
and no one remembers who currently has access.
In this case,
when Claude faithfully inherits existing permissions,
it may unintentionally expose
permission debt that otherwise went unnoticed.
Meaning the problem isn’t AI creating new issues
AI just makes it easier to actually use the
overly broad permissions that were rarely used before.
Therefore, deploying AI Connectors
is a great opportunity
to perform a permission cleanup.
You can ask three simple questions first
First:
Does this person truly need to see this data?
Second:
Does this workflow actually need to access this data?
Third:
Does AI need to take write or other actions?
Ask these questions
to progressively narrow access.
For example, creating a Monday Brief
The person might be the boss,
who has full access,
which is fine.
But the workflow only needs:
sales, cash, pipeline, invoice, and calendar data.
So Claude should only use
those specific connectors.
If only reading is required,
don’t enable write permissions.
This is the principle of least privilege.
For a proposal workflow
You may need:
CRM, past proposals, brand assets, pricing rules, and meeting notes,
but not:
payroll, bank accounts, or employee records.
Don’t connect everything simply because the boss has full access.
For marketing workflows
You may need:
campaign data, sales trends, social content, and customer reviews,
but not:
formal contracts, salaries, or complete bank transactions.
Again, segment access appropriately.
So permissions should follow the "work"
not:
"Claude is convenient, so open everything."
Every workflow
should have its own
data, tool, and action boundaries.
Even for the same person, different workflows can have different permissions
The same boss:
on a weekly brief workflow:
read-only,
on proposal workflows:
can prepare documents,
on payroll workflows:
can read data and stage it,
but actual submission is done by a human,
on marketing workflows:
can draft,
but publishing requires approval.
This is much more reasonable
than “the person is an owner, so Claude gets full access.”
Cowork itself offers different approval modes
Anthropic currently offers:
manual,
auto,
and skip modes.
The important thing is not the mode name,
but:
even if you use more automated modes,
actions configured as blocked should remain blocked,
and not suddenly become allowed.
Team/Enterprise admins can impose higher-level restrictions
For example, they may require:
write actions on a connector
always need approval,
or be completely blocked.
Users can’t override these settings.
This elevates
security boundaries
from a mere “reminder”
to real
system control.
What if small companies don’t have enterprise admins?
The principles are the same.
The boss should manage permissions personally.
Don’t connect all connectors
to the most privileged account and hope
prompts will limit access.
Prompts can say,
“don’t look at HR,”
but if the technical permissions are fully open,
that's just instructions,
not real boundaries.
Cutting permissions at the system level is better than relying on text prompts
For example:
If sending emails isn't needed,
don’t enable send permissions.
If writing isn’t needed,
set read-only.
If you don’t need a connector,
don’t connect it,
or disconnect unused connectors.
Highly sensitive data
should be inaccessible at the account level
if the workflow truly doesn’t require it.
This is more reliable than writing ten lines of "don’t do this" in prompts
Because:
prompts
are behavioral requests,
permissions
are capability limits.
If AI doesn’t have a delete tool,
it simply can’t delete.
This is far stronger than:
having the tool enabled,
then writing in prompts,
“please don’t delete.”
So that "Claude inherits original permissions" is actually good news
It means:
it shouldn’t automatically bypass
existing access controls in the source system.
But:
this is not the endpoint of permission governance.
The mature question should be one step further:
not just:
“Has Claude exceeded permissions?”
but:
“Are the person’s permissions originally too broad?”
and
“Does this AI workflow really need to inherit that much?”
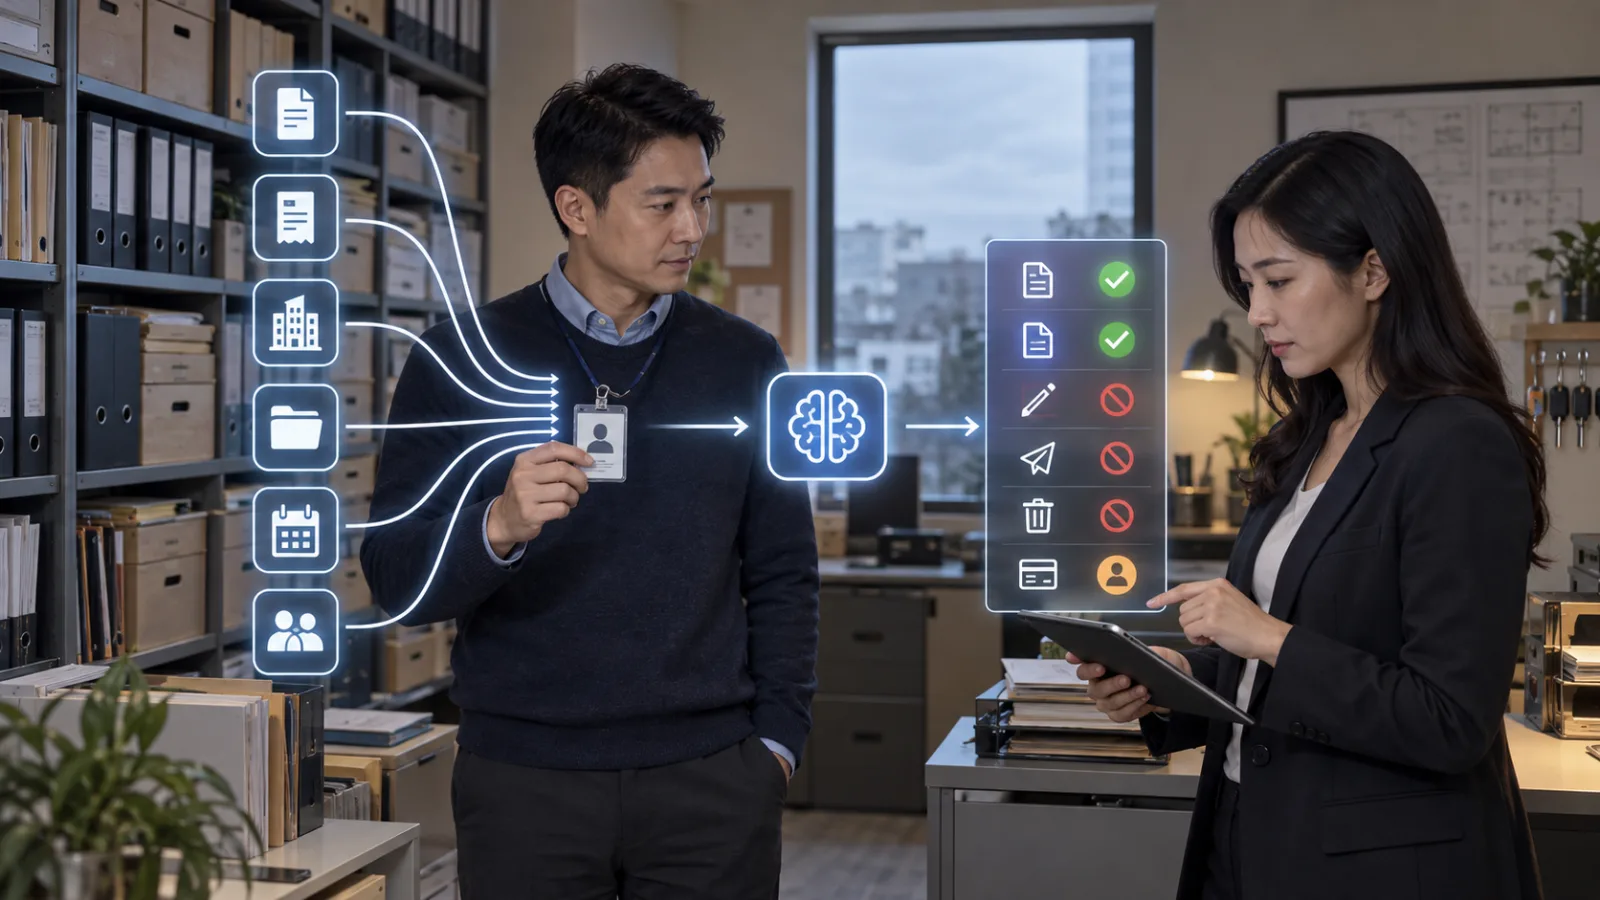
Finally, permission checks can be broken into three layers
First layer:
Human Permission.
What does this person originally have access to in the system?
Second layer:
Workflow Need.
What does this specific task actually require?
Third layer:
AI Action.
Does Claude need read, draft, write, send, delete, or pay capabilities?
Each layer
gradually narrows access.
The best result isn’t "AI has identical permissions as the person"
It is:
AI having narrower permissions.
Because:
people may need to handle many different tasks,
but an AI agent workflow usually focuses
on a narrow, specific task.
Since the task is narrower,
the permissions should be narrower too.
So the answer today is:
Claude inherits existing permissions
from QuickBooks, Drive, CRM, and other connectors.
This prevents AI from arbitrarily gaining access
it never had before.
But:
it can’t fix originally overly broad permissions.
If the account originally can see too much,
then AI likely will too.
The real solution is:
separately review:
human permissions,
workflow needs,
and AI actions.
Don’t only ask,
“Has AI exceeded permissions?”
Also ask,
“Should these permissions have existed in the first place?”
Today, let’s advance with AI.
Learn one AI tip daily.
Save a little time every day.
Improve your abilities progressively.
SasaDaily, growing alongside you.
Recommended Reading
AI One-Minute Tutorial|2026/09/01: OpenClaw’s Minimum Privilege Control for Fixed Workflows
AI Quick Q&A|2026/09/11: Does No Finding in Qodo Review Mean Merging/Deploying Is Safe?