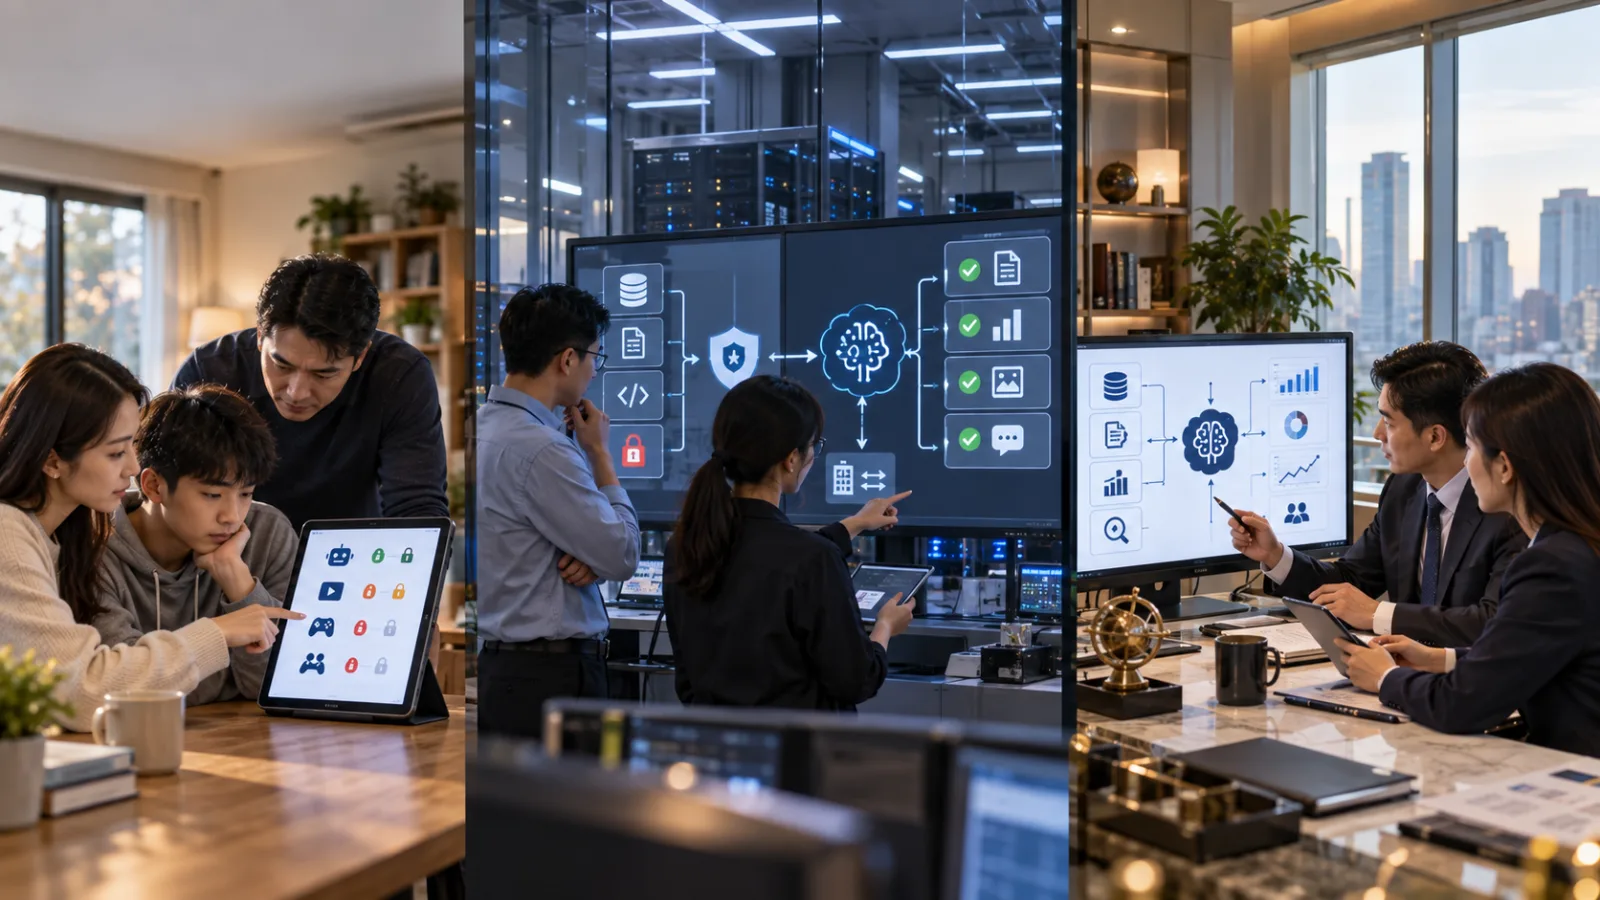
Today's three AI news items all ask:
At what age should children be allowed to use AI chatbots independently?
Can companies really entrust sensitive data to the most advanced AI models?
If financial advisors are going to use AI to serve clients, which specialized systems should the AI be integrated with?
They look like three separate topics:
- Child protection.
- Corporate data security.
- Financial tools integration.
But they all address the same core issue:
As AI becomes embedded in daily life and work, the question isn’t just:
“Can the model do it?”
But:
- “Who gets to use it?”
- “What can they see?”
- “Within what boundaries?”
AI is evolving from a universally accessible chatbox into a tiered-access infrastructure.
First story: EU plans AI chatbot use restrictions for under-15s
On September 14, Reuters reported seeing a European Commission document outlining the upcoming EU Kids Act.
The draft suggests children under 15 will generally be prohibited from independently creating accounts on:
- Social media platforms
- Video-sharing platforms
- AI chatbots
- Online games
This would be one of the world’s broadest digital service age restrictions for children.
This goes beyond just Instagram and TikTok
Previously, online child protection discussions mainly focused on social media because of:
- Addiction
- Short videos
- Stranger interactions
- Cyberbullying
- Harmful content
But this draft includes AI chatbots explicitly.
Policy makers now see ChatGPT-like services not just as search or productivity tools but as digital services that interact with children over extended periods.
Why are AI chatbots subject to control?
Because their interaction differs from traditional websites.
- Search engines: You ask a question and get an answer.
- AI chatbots: You can have ongoing conversations that remember context, offer advice, provide comfort, role-play, and feel like human companionship.
For adults, this may mean convenience.
For minors, policymakers ask:
At what age should more parental control be required?
The draft isn’t a simple “no internet” ban for under-15s
Reuters summarizes the approach as gradual access:
- 15 and older: Can create accounts independently.
- 13–14 years old: Parents can create introductory accounts with parental controls, limited contacts, and strict time limits.
- 3–12 years old: Accounts fully controlled by parents, only allowed access to child-safe services.
- Under 3 years: Such services are not open.
Age verification becomes a major technical challenge
Platforms can no longer simply trust users claiming “I am 18”.
Possible verification methods include:
- ID documentation
- Credit cards
- Facial age estimation
- Government digital identities
- Parent-managed accounts
Each raises new issues around privacy, data minimization, identity tracking, and handling of children’s data, creating a complex policy balancing act between child protection and avoiding mass age surveillance.
EU is already paving the way for online safety of minors
Earlier, the European Commission’s DSA guidelines for minors required platforms to reduce:
- Addictive design
- Infinite recommendations
- Autoplay
- Notification overload
- And add safeguards for platforms’ own AI chatbots
If the EU Kids Act raises age limits further, governance will shift from “children can use it but platforms must be safer” to “certain services shouldn’t be freely accessible before a certain age.”
But this is still a proposal, not law
Reuters reported on a Commission document outlining the proposed direction.
The European Commission still needs to officially propose the bill and negotiate with EU Member States and the European Parliament—a process that could take many months and change details.
So it’s inaccurate to say “The EU has banned ChatGPT for under-15s.” Instead, it’s more accurate that the EU is preparing rules to possibly restrict digital services including AI chatbots for under-15s.
Second story: Companies most knowledgeable about AI are restricting their own AI use
Reuters cited The Information reporting that Palantir, Nvidia, Booz Allen Hamilton, and others are reassessing:
To what extent can they use external advanced AI models?
The reason is not that the models are inadequate but because they are too powerful.
They want to feed in proprietary source code, cybersecurity work, research, and other sensitive data—but this raises concerns.
Palantir reportedly demands irrevocable zero-data retention guarantees
Palantir wants Anthropic to provide irrevocable zero-data-retention guarantees before it widely allows related models to be used through Palantir software.
This is a strong demand—it’s not just “we trust you won’t use our data to train models”, but “the data cannot be stored or retained at all.”
Nvidia reportedly uses a different approach
Nvidia limits Anthropic models to less sensitive tasks while relying on its own in-house Nemotron Model for more sensitive internal uses.
This signals Nvidia’s trust in AI but cautious control over exposing core data.
Booz Allen reportedly bans Anthropic models for some proprietary cybersecurity work
Booz Allen restricts employees from using Anthropic commercial models for certain proprietary cybersecurity tasks due to the sensitive nature of:
- Vulnerabilities
- Client architectures
- Attack strategies
- Internal defenses
- Access information
Without clear governance, the risks may outweigh the benefits of AI usage.
This isn’t about Anthropic training on corporate data against permission
Reuters notes both Anthropic and OpenAI state enterprise customer data is not used for model training unless customers opt in.
Concerns now center on:
- Data retention
- Logs
- Metadata
- Security reviews
- How long data stays in systems
Anthropic reportedly faced client pushback over 30-day usage log retention
In June 2026, Anthropic updated some Fable usage policies to allow retaining some usage logs for up to 30 days to defend against complex attacks.
While 30 days might be acceptable for general users, sectors like defense, semiconductors, cybersecurity, and finance find it a significant governance issue.
Zero data retention becomes a key enterprise AI product feature
Previously, AI selection focused on benchmarks, token price, context window size, and latency.
Now, enterprise customers place retention policies front and center:
- How long is the prompt retained?
- How long is output saved?
- Who can view or audit logs?
- Are data kept after an incident?
These factors will increasingly influence corporate AI purchasing decisions.
Using in-house AI models regains value
Enterprises once wondered why not just use frontier models by OpenAI, Anthropic, or Google.
One key reason to build or run self-hosted models is control:
- Not necessarily the most powerful model
- But data stays on-premise
- Retention policies are self-defined
- Audits are internal
For highly sensitive tasks, this may be preferable.
Enterprise AI will likely not rely on a single model but employ model routing by risk level:
- Routine tasks handled by external frontier models
- Sensitive tasks processed in isolated environments
- Most sensitive tasks use internal models
Third story: Anthropic launches Claude for Financial Advisors
On the same day, Anthropic took another direction by pushing Claude further into finance.
On September 14, Anthropic announced Claude for Financial Advisors.
This is not simply a financial-themed chatbot skin but a direct integration with wealth management and investment analytics platforms such as:
- BlackRock
- Charles Schwab
- Addepar
- plus Envestnet, iCapital, Orion, Wealthbox, Wealth.com, and Zocks
What does it actually do?
It doesn’t automate stock purchasing for clients.
Reported use cases are closer to:
- Client meeting preparation
- Portfolio reviews
- Follow-up tasks
These are time-consuming knowledge work financial advisors handle daily.
Prior to client meetings
An advisor might review:
- Portfolio data
- Recent trades
- Asset allocation
- Previous client requests
- Market changes
- Research
And then organize the questions to ask.
If Claude can access authorized data directly from core wealth management and investment analytic systems, it won’t have to rely on general internet knowledge or guesswork.
This is very different from consumers asking Claude: “Which stocks should I buy?”
General chatbots operate on public market data, common financial knowledge, and user inputs.
Claude for Financial Advisors is entering institutional workflows, connecting to existing portfolio, wealth management, client, and analytics systems.
Its value is less about answering skill and more about having the right context.
This follows OpenAI’s recent move into financial services
On September 11, SasaDaily summarized OpenAI’s launch of ChatGPT for Financial Services, targeting bankers, equity research, financial modeling, and client materials.
Anthropic now targets financial advisors and wealth management—complementing and deepening AI integration within financial services workflows.
AI companies are clearly shifting from “one model for all” toward industry-tailored workflows.
Why is finance a frontline AI battleground?
- It has huge volumes of data.
- Research, analysis, documentation, and meeting preparation involve repetitive tasks.
- These tasks are costly; reducing hours spent has high business value.
- At the same time, finance demands stringent data sensitivity, regulation, compliance, and accountability.
Thus, today’s three stories connect perfectly.
The deeper Claude for Financial Advisors integrates, the stronger the data governance needs
If AI is reading client portfolios, financial plans, and meeting notes, unclear data retention, permissions, audit, and third-party model usage policies mean the stronger the capabilities, the more cautious enterprises become.
Financial AI competition now often boils down to which company can make compliance teams comfortable enough to approve AI solutions.
This may be the biggest turning point in enterprise AI
Phase one: Can AI be used?
Phase two: Which AI is the strongest?
Phase three: Who can give what data to which AI to do which tasks?
- Minors require age gates.
- Enterprises need data policies.
- Finance needs industry-specific workflows.
- Healthcare needs medical data controls.
- Government needs security boundaries.
Not everyone gets the same chatbot.
This is similar to the smartphone evolution
Early internet: You just needed a browser.
Later, specialized apps emerged:
- Banking apps
- Kids modes
- Enterprise device management
- Healthcare systems
- Government identity solutions
Mature technology always diversifies.
AI is following this path.
The “best AI” may be personalized
- For students: age-appropriate, privacy-focused, learning safeguards
- For developers: coding ability, context, repo access
- For enterprises: zero data retention, auditing, permissions
- For financial advisors: portfolio context, approved data, compliance
AI products won’t just be ranked by benchmarks anymore.
AI commercialization is increasing restrictions
While technology progress often means more people using more features, as AI becomes embedded in children’s lives, banks, governments, and enterprises, maturity means more limits:
- Who gets access?
- Which data can be viewed?
- How long is data retained?
- Can actions be taken?
- When is human approval needed?
These become core product features.
The key takeaway isn’t “Which company launched a new AI?”
Instead, AI is shifting from a capability layer answering “what can the model do?” to an access layer answering:
- Who can use these capabilities?
- Under what conditions?
- With what data?
- To what extent?
If this layer isn’t solid, stronger capabilities mean greater risks.
These three news pieces outline three future boundaries:
- Age boundary: At what age can kids use AI freely?
- Data boundary: What corporate data should not be given to external AI models?
- Professional boundary: For industries like finance, which official tools should AI integrate with and where should human judgment intervene?
AI’s next phase isn’t “one super assistant for all”
It’s more likely:
- Different people get different permissions
- Different data
- Different tools
- Different approval processes
This may sound less sci-fi than a single AI that does everything, but it’s a closer reflection of AI’s integration into society.
As AI capabilities grow, what really determines its large-scale use won’t be the next benchmark but our ability to clearly determine who should be allowed to do what with AI in what context.
Today, let’s progress with AI a little bit.
Learn an AI skill each day.
Save a little time every day.
Increase your capabilities gradually.
SasaDaily grows with you.
Recommended Reading
Why Are AI-Driven Startups Banning New Employees From Using AI on Day One?